Burp Suite vs h5i for AI agents
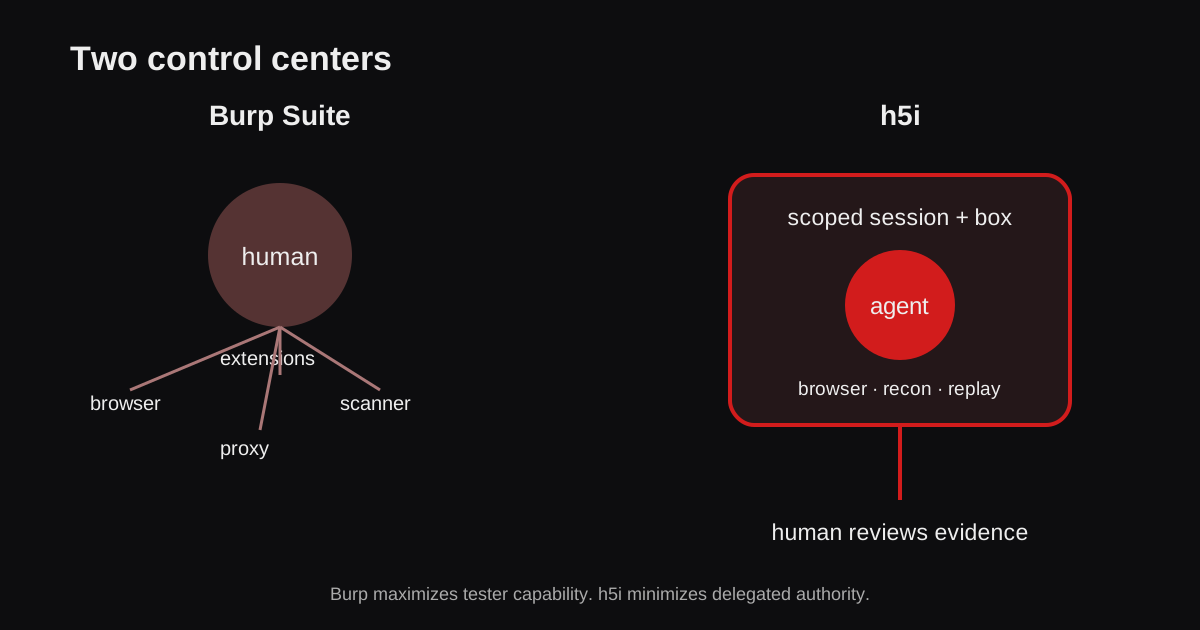
Both tools support AI-driven web testing. Burp Suite provides the deeper testing platform and its own agent; h5i is designed for fully automated penetration tests driven end to end by an external AI agent.
| Decision | Burp Suite | h5i |
|---|---|---|
| Traffic capture | Intercepting proxy records traffic from browsers and other clients | The agent browser records its own requests and responses |
| Request modification | Repeater, Intruder, Scanner, extensions | Structured edits, replay, diff, match, and sequences |
| Browser use | Mainstream browser through the proxy; Burp AT can operate Burp tools | Open, snapshot, click, fill, and inspect traffic in the same session |
| Agent interface | Burp AT inside a Burp project | CLI or JSON RPC for an external coding agent |
| Additional safety | Project scope and Burp AT tool permissions | Origin policy and an optional sandbox for the agent process tree |
Burp provides the deeper testing platform
Burp's proxy collects traffic from a full browser or another configured client. Repeater supports manual request experiments; Intruder automates payload variations; Scanner crawls and audits applications; Collaborator and extensions cover further testing workflows.
Burp AT, currently a public beta in Burp Suite Professional, gives an agent direct access to these tools and the open project's data. Burp applies project scope, lets users disable individual tools, and provides manual, smart, and autonomous approval modes. Choose Burp when testing depth, its graphical workbench, or its scanner matters.
h5i gives an external agent the complete testing loop
h5i's browser is directly controlled by the agent. The same session that opens, reads, clicks, and fills a page also records the HTTP messages. The agent can address a captured request by ID, edit a structured field, resend it, and compare the response:
$ h5i browser open https://target.example --capture --allow target.example
$ h5i browser snapshot
$ h5i browser click @e3
$ h5i browser requests
$ h5i websec replay req_42 --set query.id=456
$ h5i websec diff res_42 res_43
This is h5i's main comparison with Burp: an external agent can conduct the penetration test end to end through a direct, machine-readable path from browser action to request inspection, modification, and the next decision. h5i has fewer testing features, no vulnerability scanner, and no equivalent to Burp's extension ecosystem.
Sandboxing is an optional safety measure
For an autonomous red-team task, h5i can place the agent and browser in a box with restricted files, credentials, processes, and egress. This can limit the damage from a mistaken or prompt-injected agent. It is additional containment, not the reason h5i can capture or modify HTTP traffic; those features also work without a box.
Choose by the testing workflow
- Choose Burp Suite for the richer proxy workbench, Scanner, Intruder, Collaborator, extensions, or Burp AT.
- Choose h5i for a fully automated penetration test driven end to end by an external AI agent.
- Consider h5i's sandbox separately when that autonomous agent's host or network authority should be restricted.
Neither tool establishes authorization. For pentesting, bug bounty, red teaming, or CTF automation, the target owner or competition rules define what is allowed. Network controls help enforce part of that scope; they do not replace it.
Product references
Questions that come up
Is h5i a replacement for Burp Suite?
Can Burp Suite be used by AI agents?
Does h5i require a sandbox?
Run an authorized web security test
Create a scoped session, build an endpoint ledger, and replay one captured request.
Give the agent a narrow assignment
Make target scope, request budget, captured evidence, and the stopping point part of the run.