AI pentesting tools: Burp Suite, ZAP, Caido, or h5i?
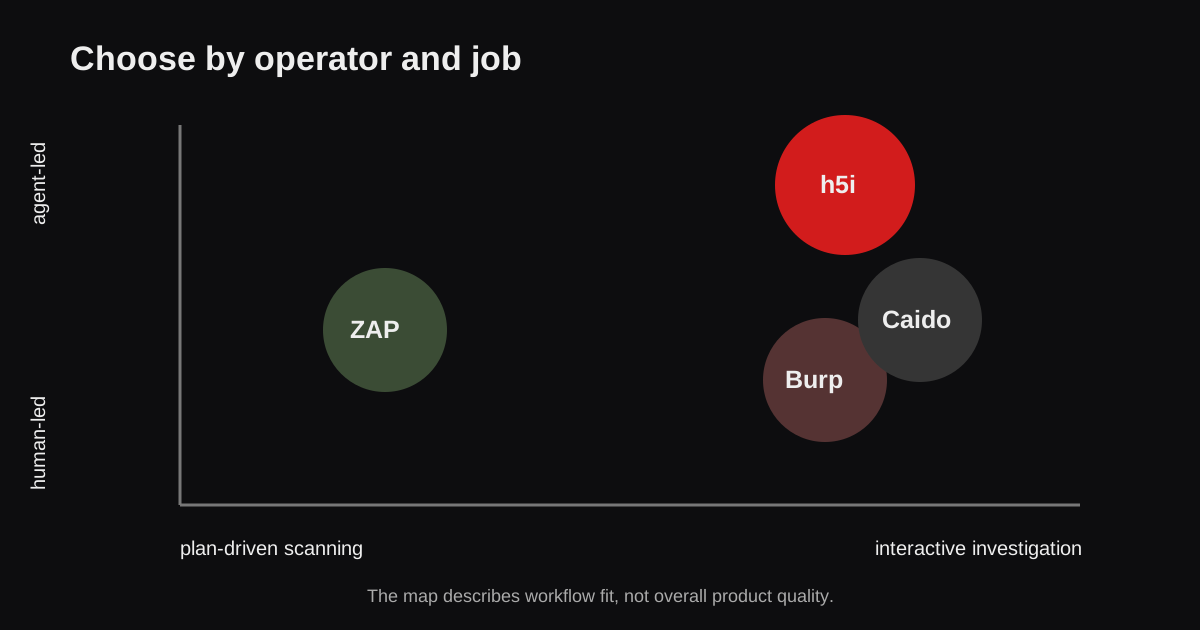
The right tool depends on what you want to delegate: help with manual testing, repeatable vulnerability scans, or an investigation where the agent chooses what to try next.
AI agents have already demonstrated strong capabilities in web security testing. Research has shown that agents can find and exploit web vulnerabilities and carry out multistep attacks (website hacking study).
Putting those capabilities to work means choosing the tools an agent will use. Should it operate Burp Suite, run ZAP scans, investigate traffic in Caido, or use a CLI-based tool like h5i?
The answer depends on what you want to delegate. This article compares the four tools through three practical uses.
What do you want AI to do?
“AI pentesting” covers several kinds of work. Consider an application that lets users download invoices.
In AI-assisted manual testing, you inspect the download request and ask a model to explain its parameters or suggest tests. You decide which requests to send and check the results.
In AI-authored automation, you ask a model to prepare a scan configuration. You review it, then run the scanner. The scan follows the configured procedure.
In agent-led testing, the agent logs in, finds an invoice, changes its identifier, compares responses, and decides what to investigate next. It needs browser interaction, HTTP request control, and enough history to track its experiments.
These approaches can overlap. They are useful starting points for choosing a tool, rather than exclusive categories.
| Your main task | A useful starting point | Why |
|---|---|---|
| Investigate a web application manually | Burp Suite | Integrated request testing tools and a large extension ecosystem |
| Run repeatable vulnerability scans in CI | OWASP ZAP | Open-source scanning with a YAML Automation Framework |
| Explore traffic and let an agent use a proxy workspace | Caido | Request search, replay, payload testing, and official agent skills |
| Let an agent browse and test through a CLI | h5i | Browser interaction and direct HTTP control in one session |
Burp Suite: a comprehensive web testing toolkit
Burp combines a proxy, browser, and tools for investigating captured traffic. You can send a request to Repeater to modify and resend it, or use Intruder to test payload variations. Burp Scanner is available in Professional and DAST. Extensions add further testing and integrations (Burp tool documentation).
For someone already working in Burp, AI can build on that familiar process: explain a response, suggest an experiment, or help automate a task. PortSwigger also documents AI features in Repeater. The details of an external agent's access depend on the integration you use.
Burp is a good starting point when you want a human to investigate findings with a broad set of tools close at hand. Read the detailed Burp Suite vs h5i comparison.
OWASP ZAP: repeatable scanning and CI automation
ZAP's Automation Framework lets you describe a scan in YAML, including authentication, crawling, passive and active scanning, reports, and exit behavior. An AI model can help prepare that configuration, while ZAP executes the jobs (ZAP Automation Framework).
This fits a recurring task such as scanning a staging application after deployment. You can review the configuration, keep it in version control, and reuse it across runs.
An agent can also use ZAP during an investigation. Its particular appeal here is that you can get automated vulnerability checks without making every testing decision depend on a live conversation with a model. Read the detailed OWASP ZAP vs h5i comparison.
Caido: a proxy workspace agents can use
Caido provides traffic search with HTTPQL, individual request experiments with Replay, and payload testing with Automate. Its workflows support reusable processing. Official Caido Skills let coding agents interact with Caido through its APIs (Caido documentation).
That makes Caido relevant to both manual and agent-assisted testing. You can investigate captured traffic yourself, then ask an agent to help with work in the same workspace.
Choose it when the proxy workflow suits you and you want an agent to use the requests and testing tools already available there. Check the installed skills and their permissions to understand what the agent can access. Read the detailed Caido vs h5i comparison.
h5i: browser interaction and HTTP testing from the terminal
h5i is a headless browser controlled through a CLI. It combines page interaction with direct HTTP request inspection and manipulation, so an agent can browse an application, inspect the requests it generates, edit and replay them, and compare responses without a separate interception proxy (h5i HTTP workbench).
For the invoice example, the agent can find the download link through the page, inspect its request, change the invoice identifier, and examine the result. Page navigation and request experiments belong to the same session.
h5i also supports destination restrictions, audit logs, and sandboxing for the browser or the surrounding workflow. Those controls matter when you want to limit an agent's access. It does not include a vulnerability scanner: the agent or tester interprets the responses and develops the tests.
Choose h5i when you want an agent to work through browser and HTTP operations from the terminal, and are comfortable letting that agent direct the investigation.
You can combine them
You do not need to commit every stage of testing to one product. A ZAP scan might produce a finding that you investigate manually in Burp or Caido. An agent using h5i might identify a suspicious authorization flow that you reproduce in Repeater.
Before choosing, ask what you need most: scanner-generated findings, an interactive traffic workspace, or browser and HTTP tools for an agent. Then check how you will authenticate, retain requests and responses, and reproduce a finding.
For work on a real target, follow the engagement or bug bounty program's scope and automation rules. Tool settings can help enforce those limits, but no tool establishes authorization.
Official sources
- PortSwigger: Burp Suite tools
- ZAP Automation Framework
- Caido Skills
- h5i HTTP workbench and recon ledger
Questions that come up
Which AI pentesting tool should I start with?
Can an agent drive the whole investigation?
Which tool should I use for automated vulnerability scanning?
Authorized web security testing with h5i
Turn target scope and request budgets into an auditable agent session.
Decide what you want to delegate
Then select the scanner, workbench, or agent session that fits it.