Caido vs h5i for AI agents
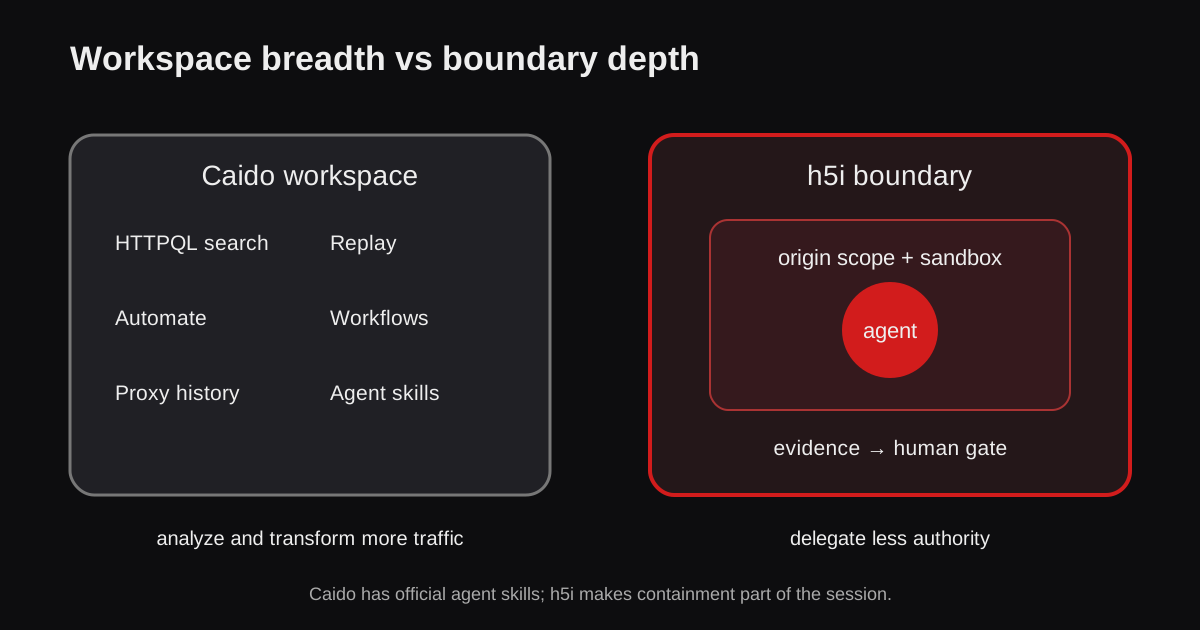
Caido gives humans and agents a complete proxy workspace. h5i is designed for fully automated penetration tests driven end to end by an external AI agent through browser and HTTP operations.
| Decision | Caido | h5i |
|---|---|---|
| Traffic model | Intercepting proxy with searchable history | Browser session with captured messages |
| Request testing | Replay, payload fuzzing with Automate, reusable workflows | Structured replay, diff, match, and sequences |
| AI interface | Official skills with complete Caido API coverage | CLI or JSON RPC called by an external agent |
| Analysis | HTTPQL over a large traffic corpus | Small endpoint ledger tied to request and response evidence |
| Additional safety | Caido access follows the connected instance and credentials | Origin policy and an optional sandbox for the agent process tree |
Caido already has strong agent support
HTTPQL filters proxied requests and responses by fields such as host, path, headers, body, status, timing, and source. Replay edits and resends individual requests. Automate runs payload sets, and workflows make processing reusable.
Official Caido Skills use the Client SDK and state that they cover the complete Caido API. An agent can search traffic, use Replay, fuzz with Automate, and operate the rest of the exposed workspace. Caido is therefore neither GUI-only nor merely “AI-assisted.” For an agent that needs a capable proxy workbench, Caido is usually the better fit.
h5i starts from an autonomous testing loop
h5i has much less testing machinery. Its browser is also the source of its HTTP record: the agent opens and operates a page, lists the resulting requests, then edits and replays a captured message by ID.
$ h5i browser open https://target.example --capture --allow target.example
$ h5i browser snapshot
$ h5i browser click @e3
$ h5i browser requests
$ h5i websec replay req_42 --set query.id=456
This direct browser-to-request path lets the external agent conduct the penetration test from exploration through HTTP experiments and follow-up decisions. Caido is better when the task starts from a large proxy history, needs expressive HTTPQL queries, or requires Automate and reusable workflows.
Sandboxing is optional
For an autonomous red-team run, h5i can place the agent and browser in a box with restricted files, credentials, processes, and egress. This is an additional way to limit agent mistakes, not the main difference in traffic capture or request testing.
Choose by the testing interface
- Choose Caido for a rich proxy UI, large-scale traffic search, request replay, payload fuzzing, workflows, or agent access to those capabilities.
- Choose h5i for a fully automated penetration test driven end to end by an external AI agent.
- Consider h5i's sandbox separately when that agent's host and network access should be restricted.
Neither product grants permission to test a target. Keep target ownership, rules of engagement, rate limits, and authorization outside the agent and visible to the reviewer.
Product references
Questions that come up
Is h5i an alternative to Caido?
Can AI agents use Caido?
What is the main architectural difference?
Burp Suite vs h5i for AI agents
Compare Burp's full testing platform with h5i's browser and HTTP command interface.
Choose by the traffic workflow
Decide whether the agent needs a full proxy workspace or a direct browser-to-request loop.