OWASP ZAP vs h5i for AI agents
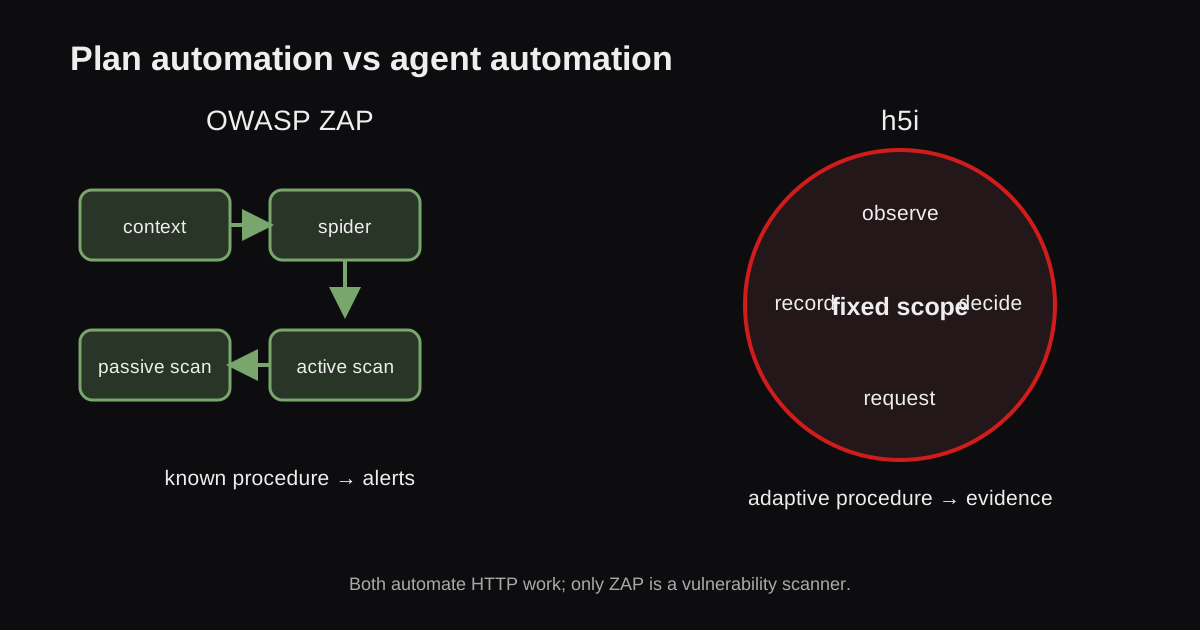
ZAP automates crawling and vulnerability scanning. h5i is designed for a fully automated penetration test in which an external AI agent explores the application and chooses each next experiment.
| Decision | OWASP ZAP | h5i |
|---|---|---|
| Main result | Alerts, scan coverage, and reports | Browser state, captured messages, endpoint evidence, and an execution receipt |
| Automation | Automation Framework, API, CLI, Docker, MCP and LLM add-ons | CLI or JSON RPC called by an external agent |
| Discovery | Traditional, AJAX, and client spiders | Small bounded crawl and evidence-linked endpoint states |
| Security testing | Passive and active scanners | Replay and comparison; no vulnerability scanner |
| Additional safety | ZAP contexts and scan policies | Origin policy and an optional sandbox for the agent process tree |
ZAP is a scanner, including when AI drives it
ZAP's Automation Framework can combine authentication, spiders, passive and active scans, API imports, tests, reports, and exit status in a YAML plan. It is suited to CI and repeatable DAST runs. Its MCP Integration add-on also lets an external AI client start spiders and scans or read alerts; the separate LLM Support add-on can invoke those MCP tools from ZAP itself.
The MCP add-on is currently alpha, and ZAP warns that its server grants broad control and must remain on localhost for trusted clients. The important point is that ZAP is not limited to fixed YAML plans and is not “non-agentic.”
h5i lets the agent drive the entire investigation
h5i lets an agent browse, capture a request, change structured fields, replay it, compare responses, and keep endpoint observations tied to messages. It does not generate vulnerability alerts or replace ZAP's scan rules.
$ h5i browser open https://target.example --capture --allow target.example
$ h5i browser snapshot
$ h5i browser requests
$ h5i websec replay req_42 --set query.id=456
$ h5i websec diff res_42 res_43
The difference is the unit of work. ZAP applies spider and scan rules and produces alerts. With h5i, the external agent drives the complete penetration-testing loop: observe the application, form a hypothesis, run an HTTP experiment, interpret the result, and choose the next action.
Sandboxing is optional
For an autonomous red-team run, h5i can also place the agent and browser in a box with restricted host and network access. This limits possible damage if the agent makes a bad decision; it is not required for traffic capture, request modification, or replay.
Choose by the required result
- Choose ZAP for open-source DAST, spidering, automated alerts, or CI reports—even if an AI agent launches the work.
- Choose h5i for a fully automated penetration test whose direction is decided continuously by an external AI agent.
- Use both when ZAP supplies scan coverage and an h5i-driven agent investigates or reproduces selected findings.
Only test systems you own or are authorized to assess. Neither a context definition nor an origin allowlist grants permission.
Product references
Questions that come up
Is h5i an alternative to OWASP ZAP?
Can an AI agent use OWASP ZAP?
Are both tools open source?
Caido vs h5i for AI agents
Compare a complete proxy workspace with an agent-driven browser and HTTP session.
Start with one scoped session
Use a target you are authorized to test and make the request ceiling explicit.